In 2024, AT&T lost sensitive communication logs of 109 million customers in a massive data breach. Call logs can reveal a lot about you, like your closest relationships, where you live and work, and your daily routine. 109 million people (nearly a third of Americans) suffered a massive data breach in April 2024 that exposed […]
In 2024, AT&T lost sensitive communication logs of 109 million customers in a massive data breach. Call logs can reveal a lot about you, like your closest relationships, where you live and work, and your daily routine.
109 million people (nearly a third of Americans) suffered a massive data breach in April 2024 that exposed their AT&T communication logs.
AT&T lost sensitive information including phone numbers, call and text counts, call durations, and location data from May to October 2022, and January 2023, meaning the data was approximately two years old at the time of the breach, impacting both current and former customers.
AT&T said the records didn’t contain call content, customer names, or Social Security numbers. That’s less reassuring than it sounds, because even on their own, call logs reveal a lot about you.
What are call logs?
Every call, text, and data session generates records inside your carrier’s network. The two kinds that matter here are:
- SIP messages. Session Initiation Protocol (SIP) manages calls and texts, both within a carrier and between networks. One message starts a session and another ends it. Carriers use them mainly to troubleshoot dropped calls and failed texts.
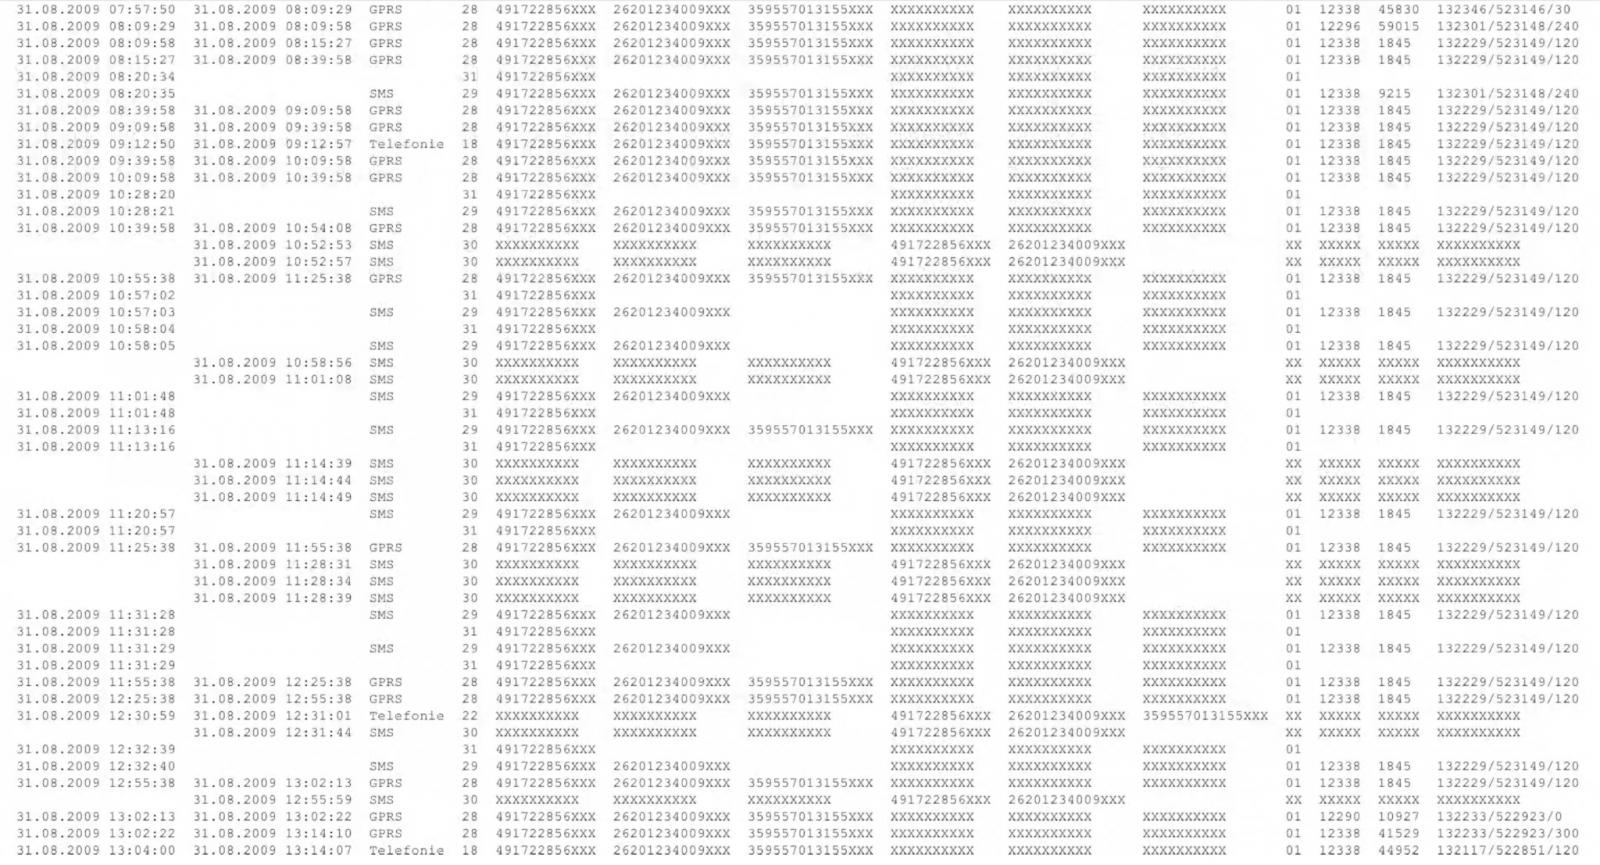
- Call Detail Records (CDRs). CDRs summarize each call, text, and data session: who was involved, when, for how long, and often which cell site your phone used. Carriers use them for billing and for settling charges with roaming partners.
Anyone with access to your call logs can identify your closest relationships, locate your home and workplace, and reconstruct your daily routine in more detail than you could yourself. If you called an oncologist a few years ago, there’s likely a record of it, how long you talked, and where you were. If you texted an old friend afterwards, there’s a log of that too.
Call metadata can even be correlated with publicly available information to derive identities.
Malte Spitz showed how far this goes. In 2011 he sued his telecom for the data it held on him, received roughly 35,000 records, and reconstructed a strikingly specific replay of several years of his activities.
Why call logs are easy to get
Three things make them an easy target.
They’re kept for a long time. Most carriers don’t say how long. Privacy policies typically promise to retain data for “as long as necessary to fulfill the purposes” of the policy. In 2022, responding to a request from the FCC chair, carriers disclosed that they kept geolocation data for as long as five years, far longer than phone service requires. One reason is to monetize it.
They sit in a few big targets. Carrier data is frequently breached. AT&T was one of many Snowflake customers hit by credential-based thefts, alongside Ticketmaster and Neiman Marcus. Salt Typhoon, the China-linked campaign, reportedly compromised every major US carrier, which could put call metadata for any American within reach.
They have other buyers. Retained logs are used to build detailed behavioral profiles that are sold to ad networks and data brokers and, in some cases, handed to the government.
The AT&T breach is the predictable result. The records were available to steal because they existed.
Protect yourself with private cell service.
Cape is America’s privacy-first mobile carrier providing unlimited talk, text, and 4G/5G data, built from the ground up with privacy and security at its core.
Most carriers track everything: where you go, who you call, what you do. Cape collects the minimum amount of information required to provide you with service, deletes call and text metadata after 24 hours, rotates your network ID to prevent tracking, defends against SIM- and network-based attacks, and more.
Privacy shouldn’t cost more. Switch today and get $29 off for life.
Cape is built to forget
Cape deletes call and text metadata in days instead of years. Unlike other MVNOs, Cape runs their own mobile core and produces their own logs, meaning they can control when logs are deleted.
Its Disappearing Call Logs feature sets a short retention window for each record type:
|
Record |
Cape |
Other carriers |
|
SIP messages |
14 days |
Months |
|
Internal CDRs |
1 day |
Years |
|
Billing CDRs |
30 days |
Years |
|
Daily totals |
60 days |
Years |
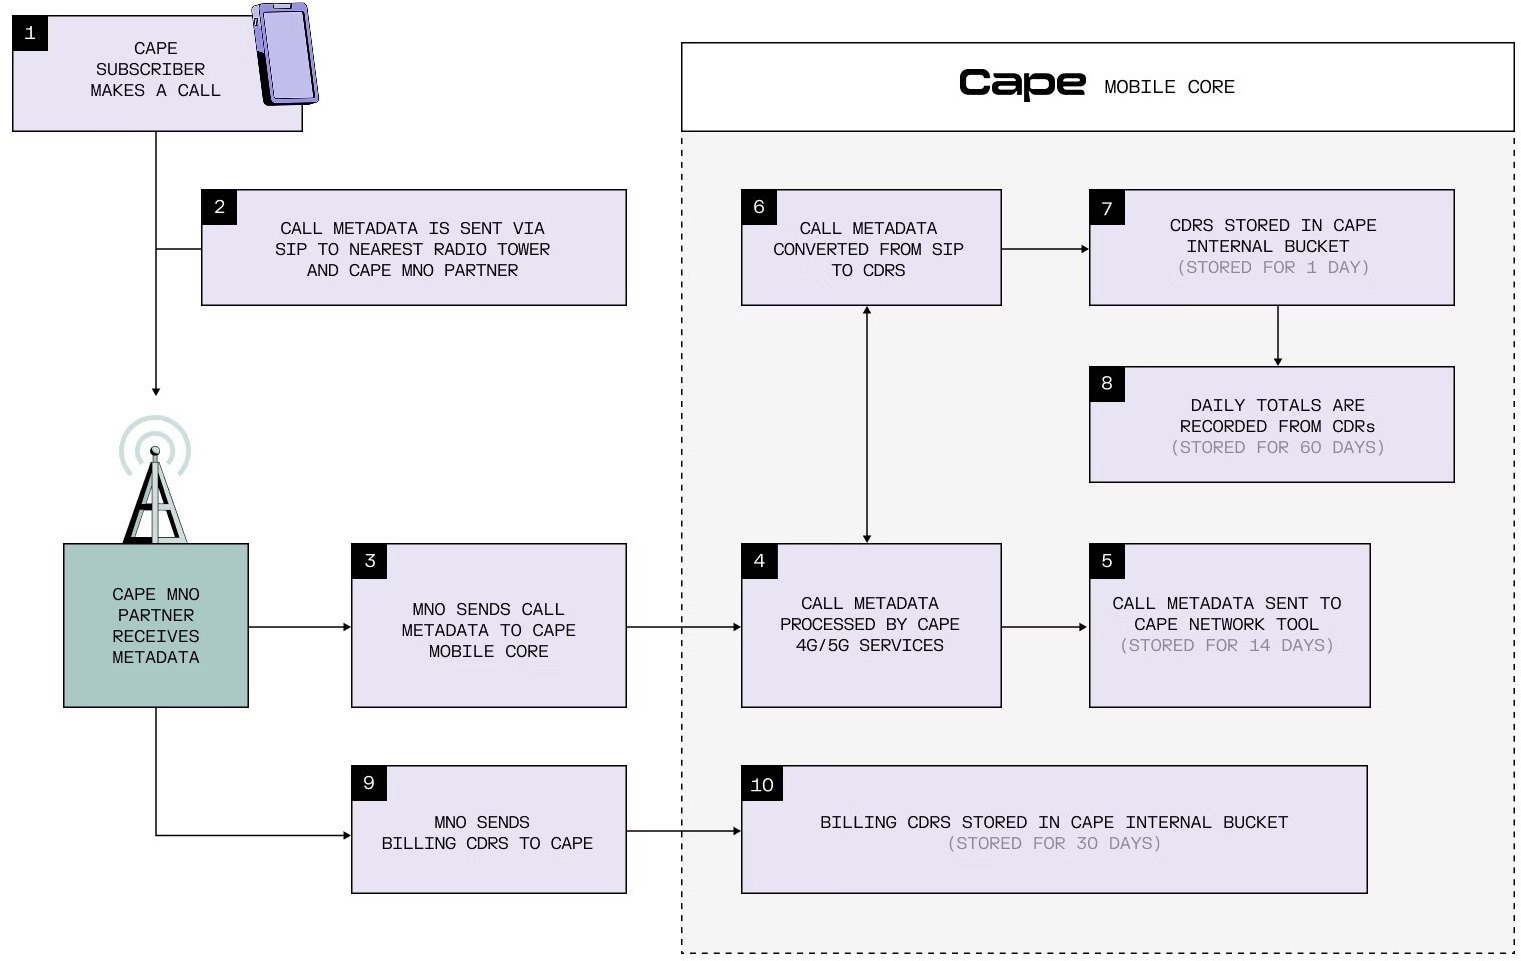
When a Cape subscriber makes a call, the signaling goes to the nearest radio tower and to Cape’s partner network operator, which passes it to Cape’s mobile core. The core forwards it to the recipient’s carrier.
Cape keeps SIP messages for 14 days to debug network issues, converts them into internal CDRs, and deletes those after one day. Daily totals (counts of calls, SMS, MMS, and data used per subscriber) are kept up to 60 days for billing and spam prevention.
CDRs sent by partner networks as billing evidence are held for 30 days, long enough to dispute a bill.
Cape’s partners and the tower operators generate logs too. For that reason Cape rotates the identifiers the towers see, which weakens their ability to tie those logs to you.
The audit
A retention claim is only worth what you can verify. Cape hired Trail of Bits to audit the feature in May and July 2026 and published the attestation.
During the audit, Trail of Bits found no evidence of violation of the two given claims:
- CDR files are being deleted within the retention policy.
- Cape does not extract or retain data from CDRs about individual consumer customers, except daily totals. Daily totals are the number of calls, number of SMS, number of MMS, and amount of data a subscriber used in a day. This data is retained for no more than 60 days and then deleted.
You can read the full audit write-up or 404 Media’s coverage.
You can’t un-breach a database, but you can shrink it
Better carrier security matters, but the more reliable control is to hold less. Records deleted days after a call can’t be stolen two years later.
For journalists, executives, security staff, and anyone who calls a doctor, lawyer, or source they’d rather not advertise, your carrier’s retention policy is part of your threat model.
Switch to a carrier that deletes your call logs. Learn more about Cape →
Sponsored and written by Cape.