



A data-wiping malware attack has forced Russian cloud services provider Beget to rebuild its cloud infrastructure from scratch, the company said. On the night of November 1st, the attacker gained access to the management systems of the company’s entire architecture and deployed malware that erased server data. The Russian cloud provider detected the attack shortly after […]
A data-wiping malware attack has forced Russian cloud services provider Beget to rebuild its cloud infrastructure from scratch, the company said.
On the night of November 1st, the attacker gained access to the management systems of the company’s entire architecture and deployed malware that erased server data.
The Russian cloud provider detected the attack shortly after the malware activated and disconnected all servers from the network to stop the malicious activity from spreading across its infrastructure.
Beget is a major Russian web-hosting, cloud, and domain-registration provider that serves more than 200,000 customers, including online stores, media, and educational services.
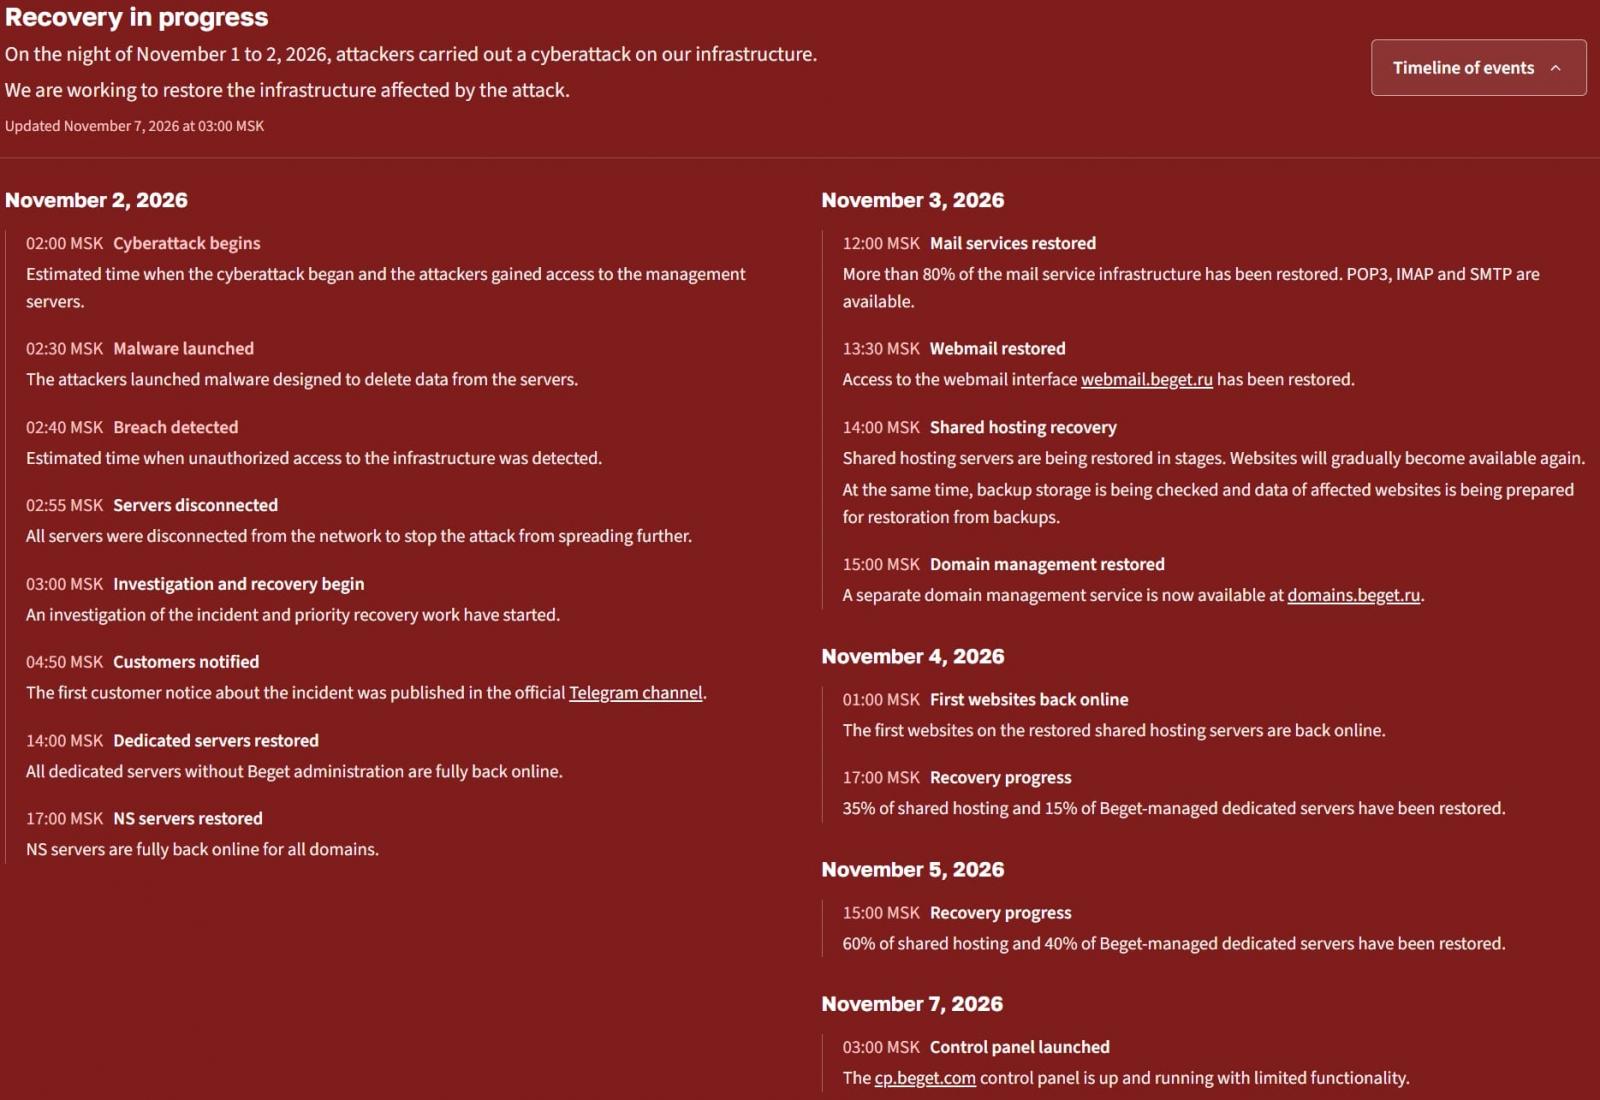
More than a week after the destructive attack, Beget says that 60% of shared hosting and 40% of the dedicated servers it manages have been restored, and recovery is still in progress.
Source: BleepingComputer.com
In a more detailed announcement on November 3, Beget says that the attacker gained access to the management layer of its entire architecture and then executed data-zeroing scripts.
Beget said all data in its cloud infrastructure, including VPS, S3, and Kubernetes, was lost, along with CDN settings and IP configurations.
The company also said that VPS binary backups were completely lost, and VPS file backups have partially survived. A November 6 assessment specified that these would be available for roughly half of its VPS users.
“Unfortunately, it is impossible to recover all data,” Beget said about VPS data, adding that it “spent a long time looking for solutions, but according to our current assessment, VPS file backups will be available for only half of users.”
Even when a backup exists, the company said it would take time to match it to specific users, a task it describes as “technically complex.”
The scale of the recovery effort is massive, with roughly 1,000 servers requiring manual checks for vulnerabilities and hidden scripts before they can be brought back online, said the firm.
Beget is taking a cautious approach, treating all parts of its infrastructure as potentially infected.
“We are therefore cleaning out everything we can and reworking every potentially vulnerable point, including those that previously did not appear to pose a risk.”
Beget said its investigation did not find any evidence that the attacker tried to download or modify any data on the compromised servers, and that the attack appears to have been focused solely on destruction.
The company has notified the police and government agencies and is also working with cybersecurity firms to remediate the incident and recover as soon as possible.
Uncover email threats your existing defenses may miss.
Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what’s getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.