French cloud and hosting provider OVHcloud is warning users that attackers compromised its open-source command-line interface (CLI) tool to distribute information-stealing malware. The attacker hijacked a developer’s GitHub account to gain access to the OVHcloud CLI repository and modify versions 0.11.0 through 0.15.0 of the tool. OVHcloud offers the CLI tool as an alternative for […]

French cloud and hosting provider OVHcloud is warning users that attackers compromised its open-source command-line interface (CLI) tool to distribute information-stealing malware.
The attacker hijacked a developer’s GitHub account to gain access to the OVHcloud CLI repository and modify versions 0.11.0 through 0.15.0 of the tool.
OVHcloud offers the CLI tool as an alternative for system administrators and developers to manage cloud and hosting services directly from a terminal, including for automating tasks.
OVHcloud CEO Octave Klaba disclosed that the company’s CLI repository on GitHub had been compromised, urging users who downloaded the latest version yesterday to update or remove the tool.
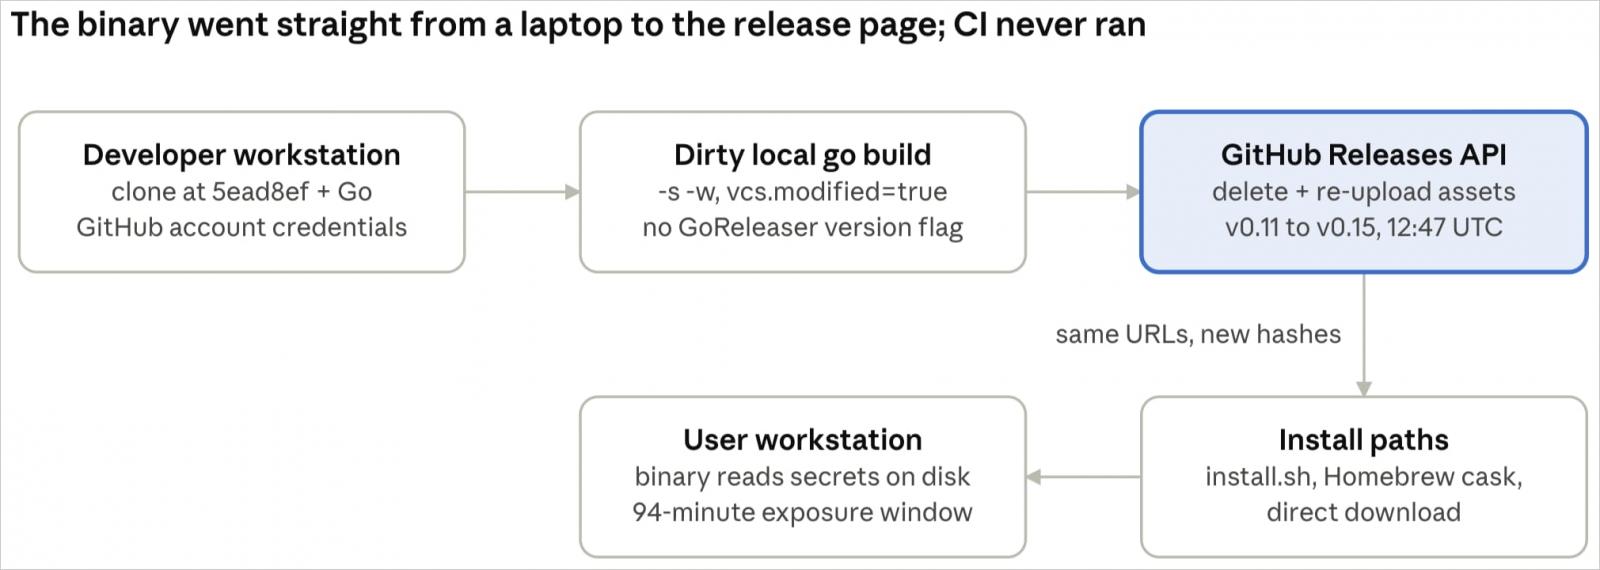
Klaba said that the compromised release appeared at 14:47 on October 19 and was detected and blocked at 16:21 after a customer reported it.
“The compromised versions are v0.11.0 v0.12.0 v0.13.0 v0.14.0 v0.15.0,” the CEO said, adding that older version 0.10.0 and the latest release 0.16.0 were clean.
Despite the poor quality of the malware, its purpose was to “retrieve secrets from the disk,” Klaba explained.
In a later update, Klaba shared that GitHub’s release immutability setting was disabled, allowing a sufficiently privileged account to modify existing releases without passing CI/CD checks.
“The entire set of CI/CD pipelines with unit tests, functional tests, CVE detection, etc., were not impacted.”
OVHcloud has enabled GitHub’s release immutability feature and considers the incident resolved.
However, Klaba urges users who downloaded a compromised CLI package to perform a system cleanup and revoke all secrets.
“The quality of the binary is poor but it can go all the way. If you are affected, please change all the secrets on your disk.”
GlassWorm connection
According to OpenSourceMalware, a community-driven threat intelligence platform, the attack was likely part of a new GlassWorm operation, known for campaigns since late 2025 that impacted the VSCode, OpenVSX, GitHub, and npm software development ecosystems.
The researchers confirmed that the attacker did not tamper with the CI/CD pipelines and uploaded malware-infected packages built locally.
Source: OpenSourceMalware
The researchers note that the GitHub account used in the attack had been compromised for more than half a year.
“Its public repositories show a scripted history rewrite on 5 March 2026 and a hidden preinstall.js loader that decodes to a second stage using a Solana memo dead drop,” OpenSourceMalware researchers found.
Although the associated wallet is a known GlassWorm indicator, the researchers did not analyze the malicious payload delivered through a trojanized version of the OVHcloud CLI.
According to OpenSourceMalware’s report, affected platforms are macOS (Intel and ARM), Linux (x86_64 and ARM64), and Windows x86-64. Source builds and Docker images remained unaffected.
Anyone who ran an affected binary should treat all secrets on the machine as compromised.

Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.