The open-source AI coding project OpenCode has notified some users that stored API keys they used with external providers were exposed in a security breach. Multiple users reported that the incident led to unauthorized API charges and suspended projects in Google Cloud. According to the project maintainer, the breach affected 1.4% of OpenCode Console users, […]
The open-source AI coding project OpenCode has notified some users that stored API keys they used with external providers were exposed in a security breach.
Multiple users reported that the incident led to unauthorized API charges and suspended projects in Google Cloud.
According to the project maintainer, the breach affected 1.4% of OpenCode Console users, with some reporting more than $1,700 in unauthorized charges overnight.
OpenCode is a model-agnostic AI coding agent that helps users understand code, write features, and fix bugs using natural-language instructions, through a terminal, desktop app, or code editor.
Users can connect AI models from multiple AI providers to the OpenCode console to streamline and automate the development process.
Distillation attack
On Saturday, OpenCode announced that it suffered a large distillation attack that impacted only developers who linked external providers, including Anthropic, OpenAI, and Google.
“We had a security breach last night related to a large-scale distillation attack that impacted 1.4% of OpenCode Console users,” the project maintainer said.
“We have notified them all this morning via email. If you did not get an email, you were not impacted, it was a subset of users who had external providers linked.”
Distillation is a legitimate machine-learning technique that trains smaller AI models using responses generated by more powerful models. The goal is to create cheaper, faster models that retain many of the capabilities of their larger counterparts.
However, the technique becomes an attack when it involves large-scale training through unauthorized queries.
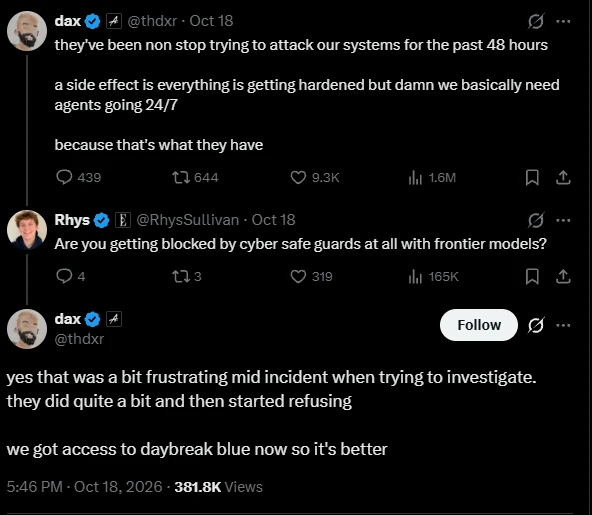
OpenCode co-founder Dax Raad said attackers had been targeting the company’s systems for at least 48 hours using AI agents.
He also said OpenCode’s investigation of the attackers were blocked when the AI models it was using began refusing requests due to built-in security safeguards.
source: Dax Raad
Raad said the situation stabilized after OpenCode began using OpenAI’s Daybreak AI cybersecurity model for defensive work, which it was approved to use on Saturday.
The email sent to impacted users notes that the earliest possible exposure of the users’ keys was on October 17, 2026, 00:30 UTC, and that no data appears to have been exposed.
OpenCode also said it was working with Google, OpenAI, and Anthropic to address the incident but could not share further details at this time.
User reports claim rogue charges following the private key leaks, ranging from several hundred USD to up to $1,700. OpenCode’s message to impacted users mentions the possibility of reimbursement for those impacted.
Some users reported that Google suspended their projects after detecting “abusive activity consistent with hijacked resources.”
BleepingComputer contacted OpenCode for more details, but we have not heard back as of publication.

Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.