Russian authorities have arrested three suspected members of a cybercriminal group known as VasyGrek in a rare public crackdown on a long-running Russian-speaking hacking operation. The group, also known as Fluffy Wolf, has been active since at least 2016 and has primarily targeted Russian companies with phishing emails designed to steal credentials, gain access to […]
Russian authorities have arrested three suspected members of a cybercriminal group known as VasyGrek in a rare public crackdown on a long-running Russian-speaking hacking operation.
The group, also known as Fluffy Wolf, has been active since at least 2016 and has primarily targeted Russian companies with phishing emails designed to steal credentials, gain access to corporate networks and deploy malware.
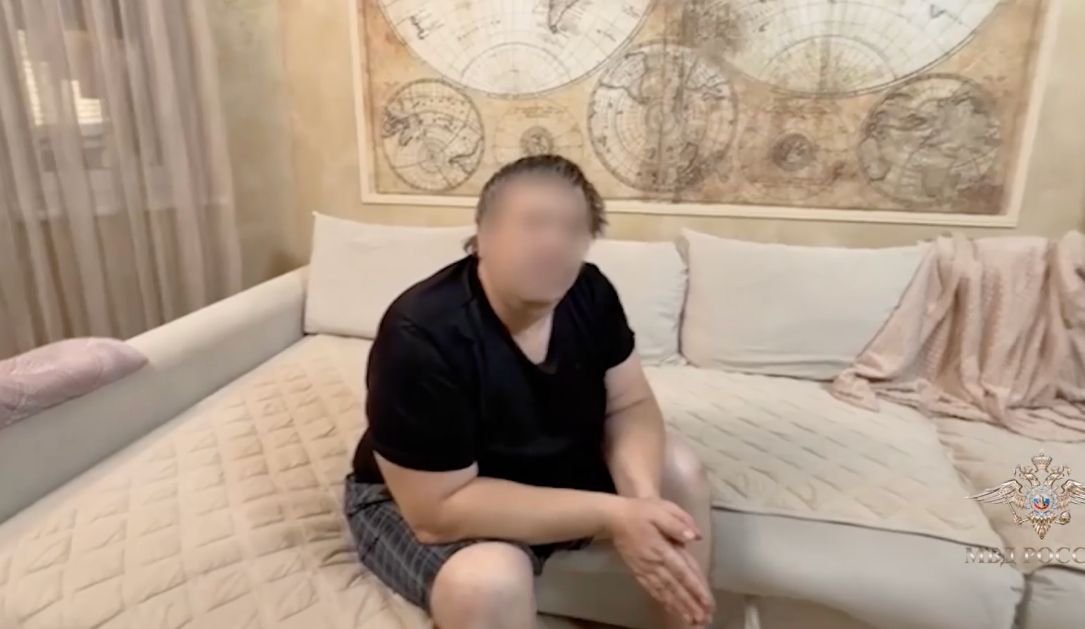
Russia’s Interior Ministry said Monday that police had dismantled the group’s infrastructure and identified its suspected members following an investigation conducted with assistance from cybersecurity firm Kaspersky.
The group’s alleged leader has been placed under house arrest, while two suspected accomplices have been released under travel restrictions, according to ministry spokesperson Irina Volk.
Such arrests are unusual in Russia, where many well-known Russian-speaking hacking groups have operated for years despite being closely monitored by cybersecurity researchers and law enforcement agencies.
Volk said the group’s activities had attracted the attention of law enforcement agencies in Russia, the United States and Europe, but did not elaborate on whether foreign authorities had assisted in the investigation.
The hackers relied on an extensive network of phishing websites impersonating financial and accounting services, as well as servers hosted abroad, authorities said. They also purchased remote administration tools on dark web marketplaces to gain covert access to victims’ computers.
In one attack described by investigators, an employee in the accounting department of an unnamed company received an email in September 2025 that appeared to come from a business partner. The message contained a malicious attachment disguised as a routine financial document.
When the employee opened the file, the hackers allegedly gained remote access to the computer and the company’s online banking system. They subsequently transferred more than 660,000 rubles ($8,000) to accounts under their control, according to the Interior Ministry.
Police searched the suspects’ homes and offices, seizing computers, communications equipment and other evidence.
The crackdown came as VasyGrek appeared to be expanding its activities beyond Russia.
In research published Monday, Kaspersky said it had detected more than 100 attempted attacks attributed to the group between January and September 2026, targeting organizations in Russia, Belarus and Kazakhstan.
The hackers most frequently targeted metallurgical companies, wholesale suppliers of raw materials and industrial goods, and government agencies, according to the researchers. Other targets included organizations in the healthcare, oil and gas, energy, finance and agriculture sectors.
Kaspersky described VasyGrek as a financially motivated cybercriminal group whose operations relied heavily on targeted phishing and malware designed to provide remote access to corporate systems.
The suspects face charges related to theft and the creation or distribution of malicious software. If convicted, they could face up to 10 years in prison on the theft charge and up to five years on the malware charge.
The Interior Ministry said the group’s hacking infrastructure had been dismantled, although it remains unclear whether the arrests will permanently end its operations
No previous article
No new articles

Daryna Antoniuk
is a reporter for Recorded Future News based in Ukraine. She writes about cybersecurity startups, cyberattacks in Eastern Europe and the state of the cyberwar between Ukraine and Russia. She previously was a tech reporter for Forbes Ukraine. Her work has also been published at Sifted, The Kyiv Independent and The Kyiv Post.