IDENTOS has announced that PolicyArc is now generally available. The new solution gives security, platform, and compliance teams a single place to define, enforce, and audit access policy across their applications. PolicyArc is built to solve how to safely extend access not just to people and services but to the AI agents now acting on […]
IDENTOS has announced that PolicyArc is now generally available. The new solution gives security, platform, and compliance teams a single place to define, enforce, and audit access policy across their applications. PolicyArc is built to solve how to safely extend access not just to people and services but to the AI agents now acting on their behalf.
PolicyArc builds on more than 12 years of IDENTOS identity and access work across Canadian government and healthcare systems.
Why now
Companies are adopting AI agents that act inside their systems, pulling data, taking actions, and making decisions. Traditional access control wasn’t built to give an agent just enough access, for just long enough, and nothing more.
According to IBM and Ponemon Institute’s 2026 Cost of a Data Breach Report, 92% of organizations that experienced an AI-related breach lacked proper AI access controls. PolicyArc is designed to address that risk, along with a more familiar challenge: access policies that are slow to change and difficult to audit.
What PolicyArc does
- Safe access for AI agents. People can grant an AI agent a scoped, time-limited version of their own access. It’s enough for the agent to do its job, and it’s automatically revoked when the task or window ends.
- Consent, enforced every time. Access isn’t just checked against policy; it’s checked against what the data owner has actually agreed to, on every request, not just at login.
- Decisions based on what’s happening right now. Access decisions combine standing facts (a person’s role, whether they’ve verified their identity) with real-time context (how sensitive the resource is, what stage a workflow is in) to allow, deny, or ask for extra verification in the moment.
- One policy, everywhere, updated in minutes. Define a resource type once and the policy applies consistently across every connected application. New resource types and policies can be added without rewriting integrations, so access rules keep pace with the product instead of trailing behind it.
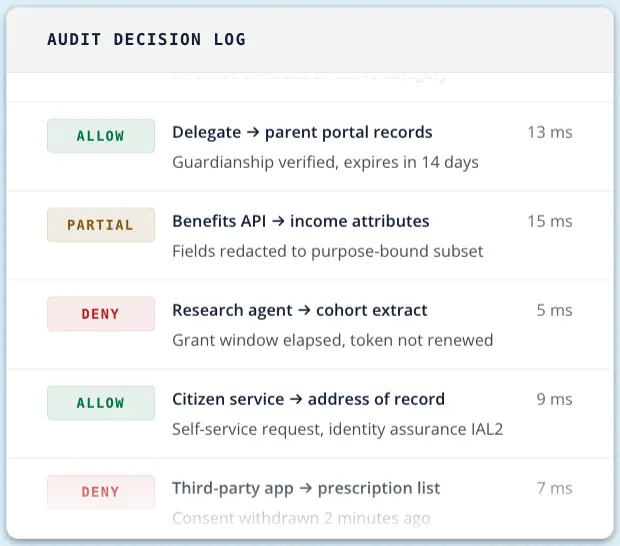
- An audit trail by default. Every access decision is automatically logged and reportable. Audit and compliance evidence exists from day one, instead of being reconstructed after the fact.
Who it’s for
PolicyArc is built for the teams who own access decisions and have to answer for them: platform and security engineering leads managing authorization across a growing product surface, compliance and risk leaders who need to prove access was appropriate, and teams shipping AI-agent features who need a safe way to delegate access without building that infrastructure themselves.
“Most systems only know how to grant broad, standing access. That’s fine for a person, but reckless for an agent. We built PolicyArc so a team can hand an agent exactly the permission it needs for one task, nothing more. When the task ends, the access disappears, and every decision is on record,” said Alec Laws, CTO, IDENTOS.